The Evolution of Ransomware

From Malware to Identity Warfare

Ransomware has fundamentally shifted. Attackers are no longer just breaking into environments — they are logging in. This is the new ransomware reality.

1 page

Download the eBookPDF · 1 page
The Evolution of Ransomware cover
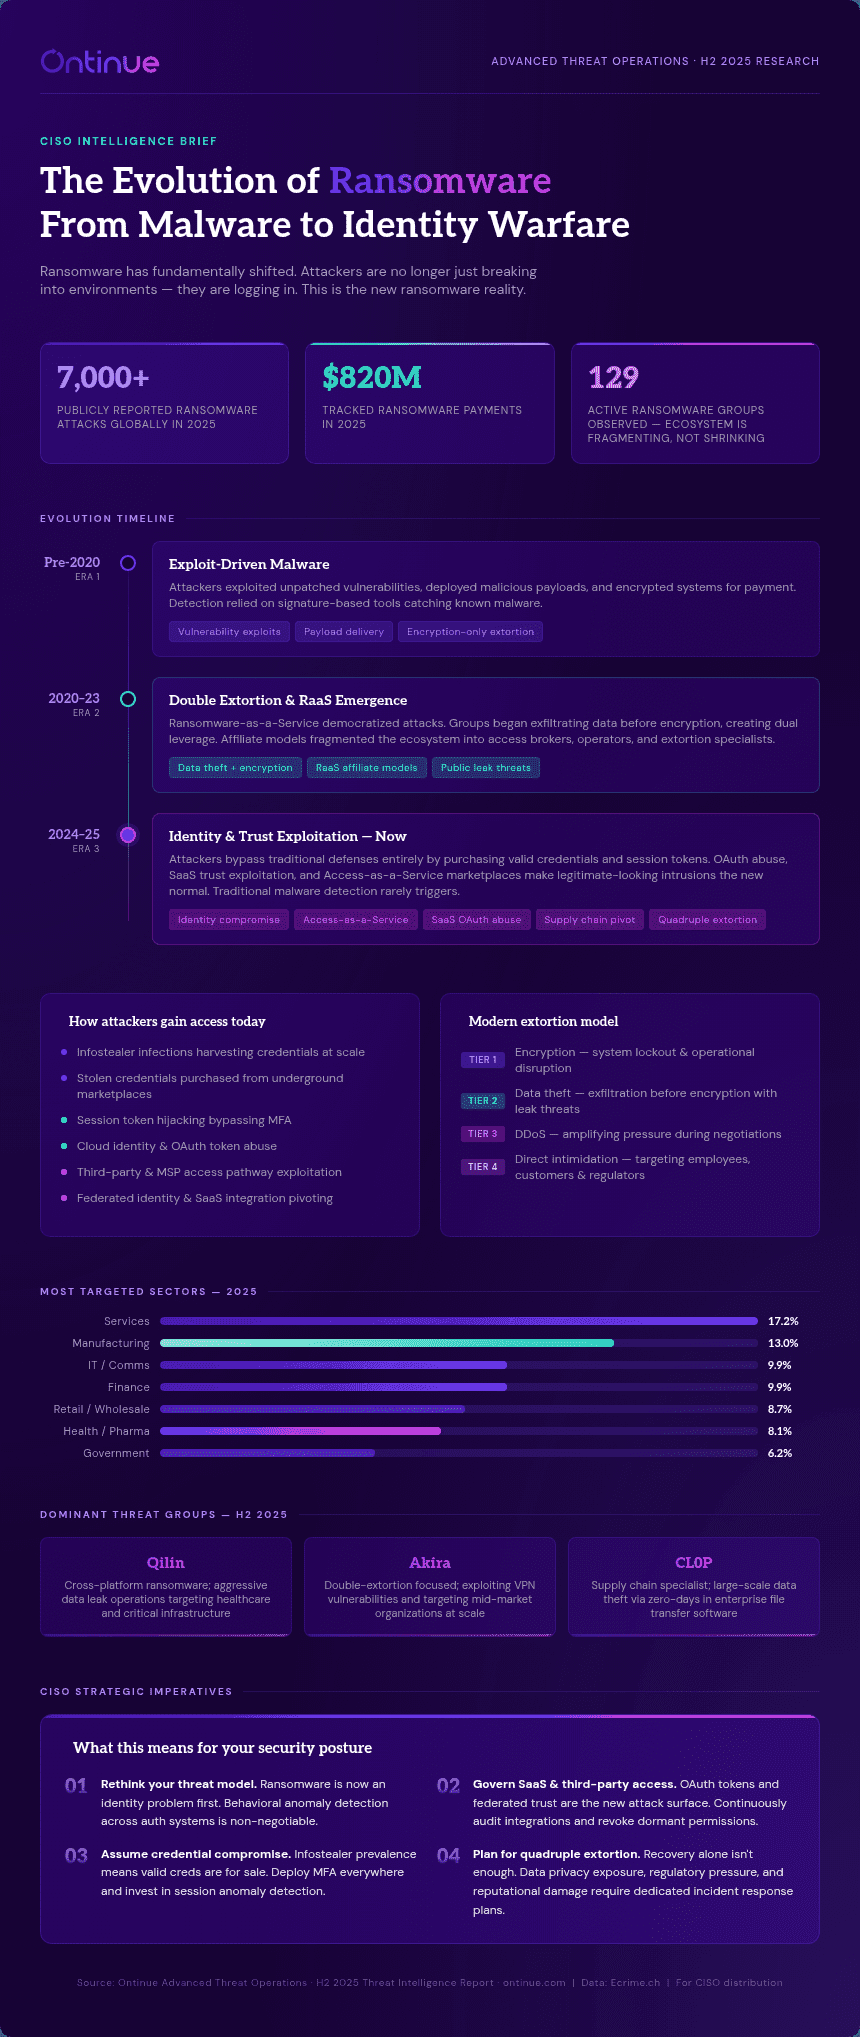
The Evolution of Ransomware infographic (Ontinue, H2 2025): three headline stats, a three-era timeline from exploit-driven malware to identity and trust exploitation, access methods, the four-tier extortion model, most targeted sectors, three threat groups and four CISO imperatives. The full text follows.

ADVANCED THREAT OPERATIONS · H2 2025 RESEARCH
CISO INTELLIGENCE BRIEF

7,000+
PUBLICLY REPORTED RANSOMWARE ATTACKS GLOBALLY IN 2025

$820M
TRACKED RANSOMWARE PAYMENTS IN 2025

129
ACTIVE RANSOMWARE GROUPS OBSERVED — ECOSYSTEM IS FRAGMENTING, NOT SHRINKING

EVOLUTION TIMELINE

Exploit-Driven Malware

Pre-2020
ERA 1

Attackers exploited unpatched vulnerabilities, deployed malicious payloads, and encrypted systems for payment. Detection relied on signature-based tools catching known malware.

  • Vulnerability exploits

  • Payload delivery

  • Encryption-only extortion

Double Extortion & RaaS Emergence

2020–23
ERA 2

Ransomware-as-a-Service democratized attacks. Groups began exfiltrating data before encryption, creating dual leverage. Affiliate models fragmented the ecosystem into access brokers, operators, and extortion specialists.

  • Data theft + encryption

  • RaaS affiliate models

  • Public leak threats

Identity & Trust Exploitation — Now

2024–25
ERA 3

Attackers bypass traditional defenses entirely by purchasing valid credentials and session tokens. OAuth abuse, SaaS trust exploitation, and Access-as-a-Service marketplaces make legitimate-looking intrusions the new normal. Traditional malware detection rarely triggers.

  • Identity compromise

  • Access-as-a-Service

  • SaaS OAuth abuse

  • Supply chain pivot

  • Quadruple extortion

How attackers gain access today

  • Infostealer infections harvesting credentials at scale

  • Stolen credentials purchased from underground marketplaces

  • Session token hijacking bypassing MFA

  • Cloud identity & OAuth token abuse

  • Third-party & MSP access pathway exploitation

  • Federated identity & SaaS integration pivoting

Modern extortion model

  • TIER 1 Encryption — system lockout & operational disruption

  • TIER 2 Data theft — exfiltration before encryption with leak threats

  • TIER 3 DDoS — amplifying pressure during negotiations

  • TIER 4 Direct intimidation — targeting employees, customers & regulators

MOST TARGETED SECTORS — 2025

  • Services 17.2%

  • Manufacturing 13.0%

  • IT / Comms 9.9%

  • Finance 9.9%

  • Retail / Wholesale 8.7%

  • Health / Pharma 8.1%

  • Government 6.2%

DOMINANT THREAT GROUPS — H2 2025

Qilin

Cross-platform ransomware; aggressive data leak operations targeting healthcare and critical infrastructure

Akira

Double-extortion focused; exploiting VPN vulnerabilities and targeting mid-market organizations at scale

CL0P

Supply chain specialist; large-scale data theft via zero-days in enterprise file transfer software

CISO STRATEGIC IMPERATIVES

What this means for your security posture

  1. Rethink your threat model. Ransomware is now an identity problem first. Behavioral anomaly detection across auth systems is non-negotiable.

  2. Govern SaaS & third-party access. OAuth tokens and federated trust are the new attack surface. Continuously audit integrations and revoke dormant permissions.

  3. Assume credential compromise. Infostealer prevalence means valid creds are for sale. Deploy MFA everywhere and invest in session anomaly detection.

  4. Plan for quadruple extortion. Recovery alone isn't enough. Data privacy exposure, regulatory pressure, and reputational damage require dedicated incident response plans.

Source: Ontinue Advanced Threat Operations · H2 2025 Threat Intelligence Report · ontinue.com | Data: Ecrime.ch | For CISO distribution

Recommended next.

All resources

eBook

1H 2026 Threat Intelligence Report

1H 2026 findings reveal growing abuse of trusted identities, AI-assisted tooling, SaaS platforms, and business workflows as attackers achieve greater impact…

20 min read

Read

eBook

1H 2026 Threat Intelligence Report

1H 2026 findings reveal growing abuse of trusted identities, AI-assisted tooling, SaaS platforms, and business workflows as attackers achieve greater impact…

20 min read

Read

eBook

1H 2026 Threat Intelligence Report

1H 2026 findings reveal growing abuse of trusted identities, AI-assisted tooling, SaaS platforms, and business workflows as attackers achieve greater impact…

20 min read

Read

Beyond the Perimeter: What Security Teams Are Missing

Blog

Beyond the Perimeter: What Security Teams Are Missing

Exposed credentials from a 3rd party breach and brand impersonation are two ways threat actors are exploiting organizations.

5 min read

Read

Beyond the Perimeter: What Security Teams Are Missing

Blog

Beyond the Perimeter: What Security Teams Are Missing

Exposed credentials from a 3rd party breach and brand impersonation are two ways threat actors are exploiting organizations.

5 min read

Read

Beyond the Perimeter: What Security Teams Are Missing

Blog

Beyond the Perimeter: What Security Teams Are Missing

Exposed credentials from a 3rd party breach and brand impersonation are two ways threat actors are exploiting organizations.

5 min read

Read

Ontinue Offers new Dark Web Monitoring service for ION MXDR Customers

Webinar

Ontinue Offers new Dark Web Monitoring service for ION MXDR Customers

Exposed credentials and lookalike domains surface long before an attacker moves. See how ION for Dark Web Monitoring brings those findings into your MXDR…

23 min watch

Watch

Ontinue Offers new Dark Web Monitoring service for ION MXDR Customers

Webinar

Ontinue Offers new Dark Web Monitoring service for ION MXDR Customers

Exposed credentials and lookalike domains surface long before an attacker moves. See how ION for Dark Web Monitoring brings those findings into your MXDR…

23 min watch

Watch

This is Nonstop SecOps.

Ontinue

European HQ

Grubenstrasse 54
8045 Zürich

North America HQ

450 Maple Street
Redwood City, CA 94063

UK Office

9 Holborn
London, EC1N 2LL

APAC Office

World Trade Tower, Sector 16
Noida, Uttar Pradesh 201301

Düsseldorf Office

Speditionstraße 2
40221 Düsseldorf, Germany

Vienna Office

Kohlmarkt 8-10
1010 Wien, Austria

Toronto Office

6060-3080 Yonge St
Toronto, ON M4N 3N1

Ontinue

© 2026 Ontinue. All rights reserved.

Ontinue offers nonstop SecOps through an AI-powered managed extended detection and response (MXDR) service. Ontinue ION MXDR combines powerful proprietary AI with the industry’s first collaboration with Microsoft Teams to continuously build a deep understanding of our customers’ environments, informing how we prevent, detect, and respond to threats.

Continuous protection. AI-powered Nonstop SecOps. That’s Ontinue.